Make theSIEM worth it
Managed SIEM service that assesses your detections, investigates what fires, and carries threats through resolution in the SIEM you already own.

Your SIEM can’t run itself
SIEMs go under-operated. Someone still has to keep
detections useful, investigate, and know when to act.
Detections need attention
What worked yesterday doesn’t always work tomorrow. Keeping detections useful takes continuous evaluation and tuning.
Investigation goes beyond the SIEM
Your SIEM only knows what gets sent to it. Getting to a verdict means pulling in the context that lives elsewhere.
Your rules aren’t generic
Custom detections exist because your risks aren’t generic. Investigating them well means understanding what your team built and why.
A security operation on top of your SIEM
Daylight runs the detections you already have, adds the custom ones you need, and handles the work from alert through resolution.
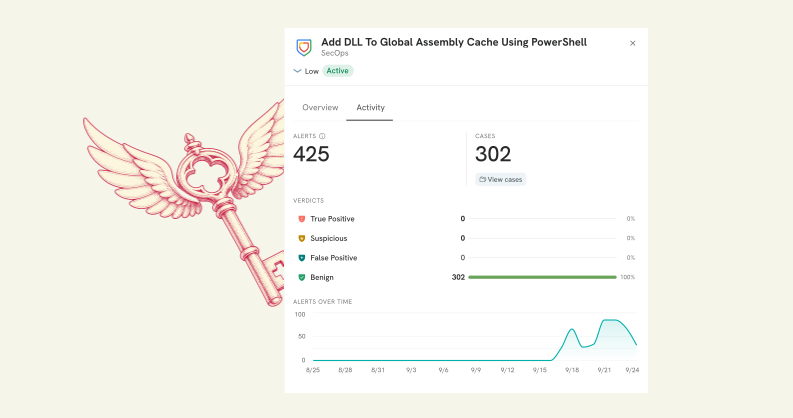
Assess the detections in your SIEM for quality, volume, and investigation readiness, so you know what’s providing coverage and what needs attention.
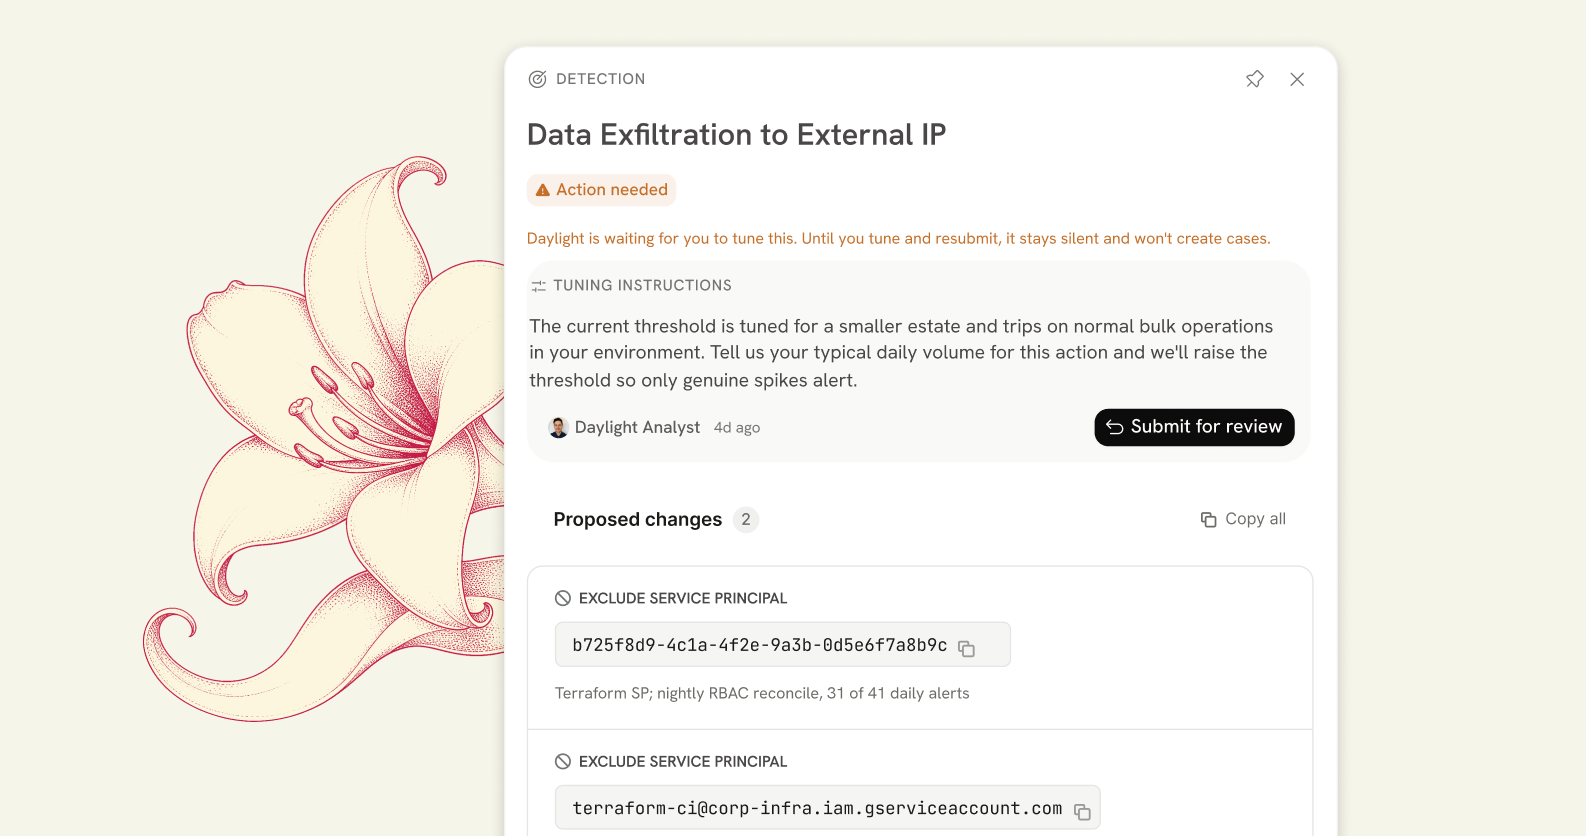
Cut noise and false positives while preserving the coverage that matters.
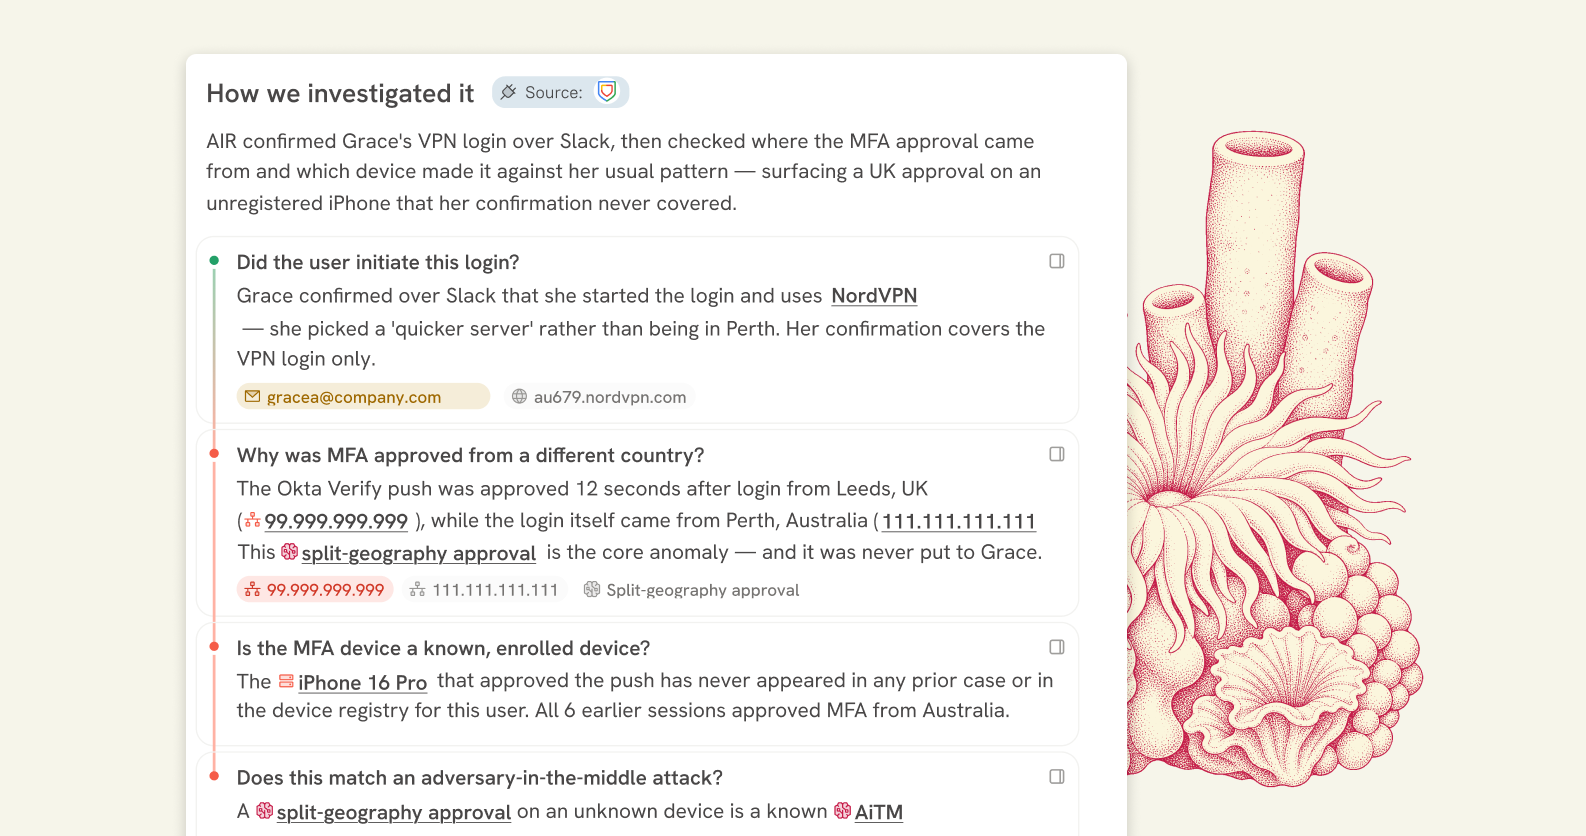
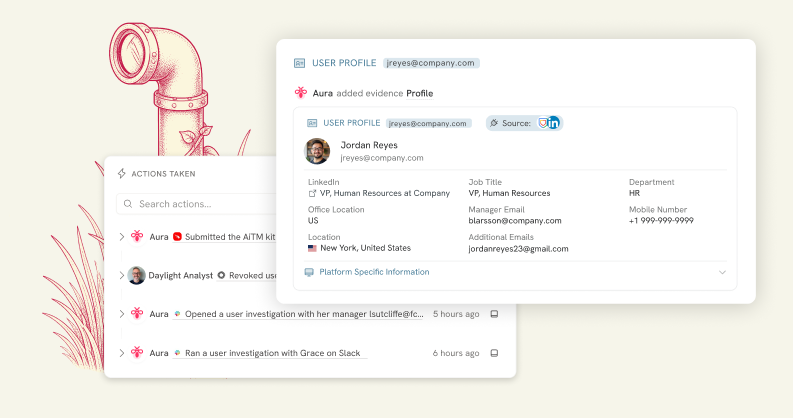
Investigate what fires using context from the SIEM and the security tools around it.
Make your SIEM earn its keep
Daylight takes what fires in your SIEM, adds the context from across your environment, and investigates it through verdict and response.

Detections coverage
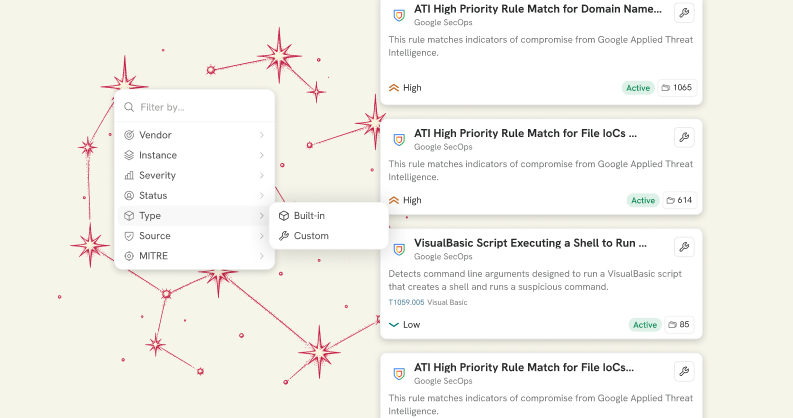
See what your SIEM is actually watching. Daylight maps every rule against MITRE ATT&CK, shows where coverage is strong and where it's missing, and recommends what to tune or add—so your SIEM fires on what matters.
See behind every rule
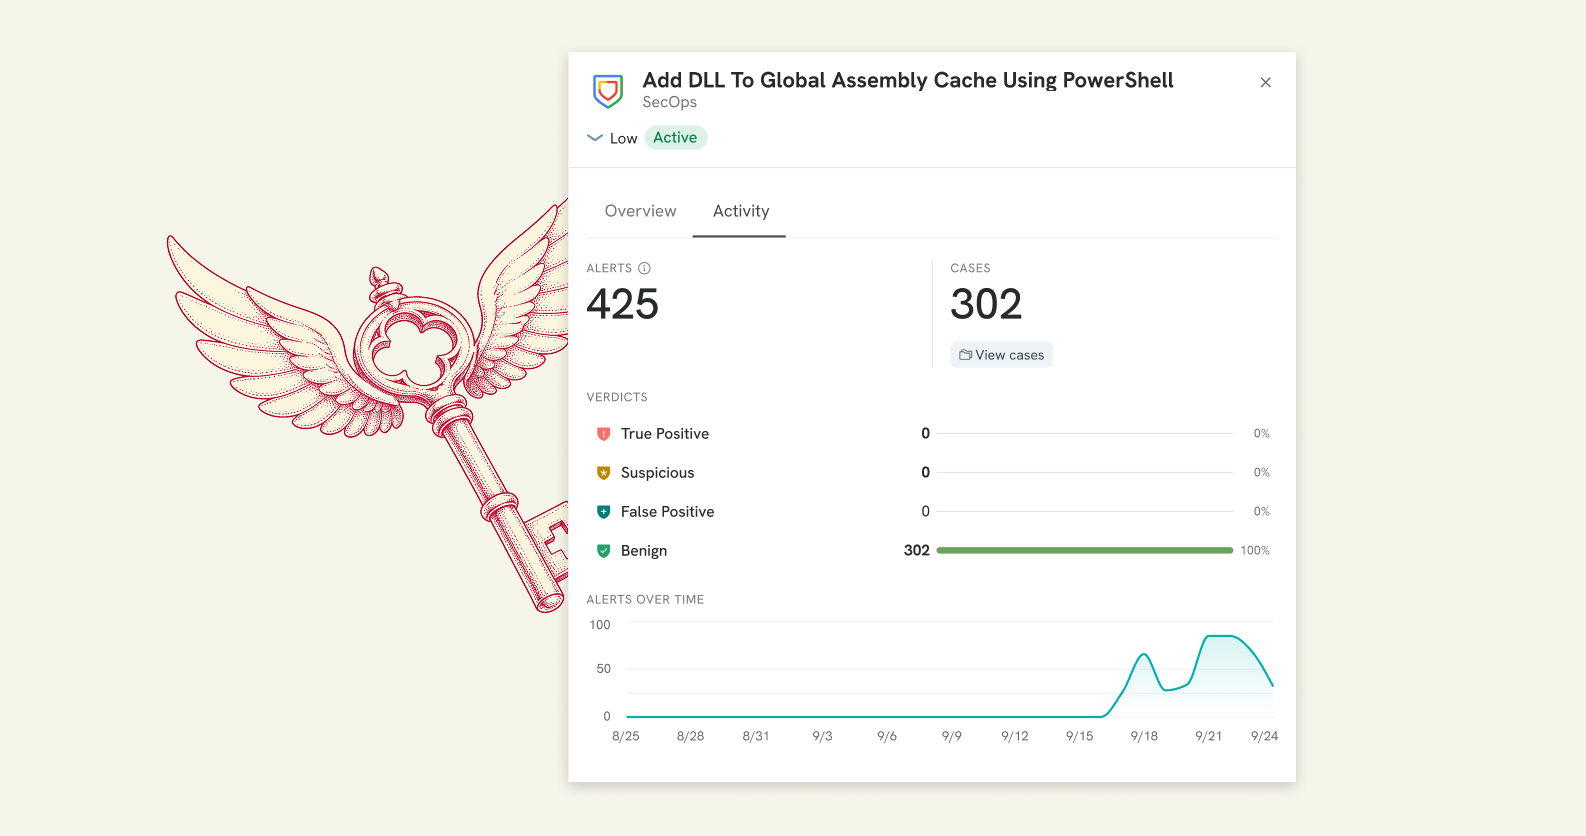
For each rule, Daylight shows what it really produces: how often it fires, how many alerts turn out to be real, and how that changes over time.
From alert to answer
Nothing your SIEM fires goes unworked. Daylight enriches each alert with context from across your environment—identity, endpoint, cloud—investigates it, delivers a verdict, and drives the response. Your SIEM keeps detecting; Daylight does everything after.
More from the SIEM you already own
Keep detections sharp. Investigate what fires. Resolve real threats.
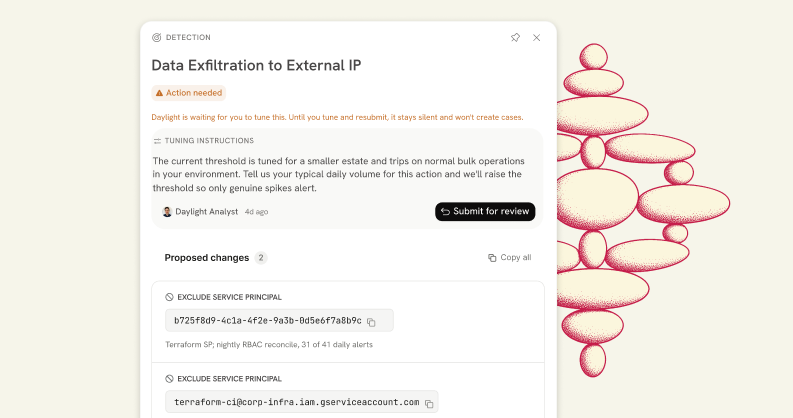
Daylight assesses the detections in your SIEM, identifies noise and false positives, and keeps
you clear on what’s working, what needs
tuning, and why.
Every supported SIEM alert is investigated using context from the SIEM and directly connected security sources, with real threats carried through response.
Daylight works with your team to understand the risk behind custom detections, validate the logic, and build the right investigation approach.
The SIEM stays, the workload changes
Compare what your team still has to own after the SIEM is up and running.
Capability
Daylight
Traditional MDR / MSSP
Self-Managed SIEM
More from every detection
Turn the detections you already have into better coverage,
deeper investigations, and clearer decisions.
Unified Detection Visibility
See Daylight, SIEM, and custom detections together, with status, activity, and MITRE coverage across your environment.
Full-Context Investigation
Enrich SIEM alerts with data from directly connected security sources, so investigations aren't limited to what was ingested into the SIEM.
Custom Detection Support
Daylight learns the intent behind your custom detections, validates their logic, and builds an investigation approach around the risk they were designed
to catch.
Multi-SIEM Coverage
Run Splunk, Sentinel, or multiple SIEMs. Daylight brings their detections and alerts into one investigation layer instead of leaving your team to work across them separately.
Explained
Decisions
Every detection assessment has a clear outcome and reason, so you can see what Daylight supports, what needs tuning, and why.
Security work doesn’t stop at managed SIEM
Agentic Threat Hunting
Continuous IOC- and hypothesis-based hunts across your environment.
Agentic Security Data Lake
The essentials of a SIEM without the complexity and cost.
Agentic MDR
Continuous investigation and response across your entire environment.
Proof over promises
Hear from the security leaders putting Daylight to work.
“Standing up an equivalent operation internally would mean building a SOC with detection engineering, threat hunting, incident response, and round-the-clock monitoring. That is a multi-year organizational build. Daylight delivered that maturity on day one.”
“We're not just buying alert triage. We're getting a team that actually understands our environment and thinks about our risk the way we do. That's the difference between a vendor and a partner.”
“I don’t need to hire another engineer. I know Daylight can handle it.”
Get more from what you’ve got



Frequently asked questions
Managed Security Information and Event Management (SIEM) is a service that operates, maintains, and optimizes an organization's SIEM environment. It typically includes detection engineering, rule tuning, monitoring, investigation, and ongoing improvements. Managed SIEM helps organizations get more value from existing security data and detections without handling every operational task internally.
Daylight's Managed SIEM service works with the SIEM you already own, so replacing your existing platform is not required. Daylight manages and tunes detections within your environment, combining AI agents with security engineering expertise to investigate and respond to threats. This preserves your existing SIEM investment while reducing operational workload.
Daylight supports collaborative SIEM operations through its flexible service models. With Co-Managed services, your team can retain ownership of selected detections, processes, and responsibilities while Daylight manages the rest. A Forward-Deployed Engineer (FDE) can also work directly with your team, adapting to your environment and established workflows.
A security data lake complements a SIEM by providing scalable storage and access to security telemetry for investigation, hunting, and historical analysis. The SIEM typically handles detection rules, correlation, and alerting, while the data lake supports broader analytical workloads. Together, they can improve visibility and reduce dependence on expensive SIEM storage.
Daylight's Managed SIEM service includes detection engineering, detection tuning, investigation, and response within the SIEM you already own. Its AI agents and security engineers work together to improve detection quality, investigate suspicious activity, and maintain effective security workflows. Customers can retain selected responsibilities or have Daylight manage the work.
Daylight reduces SIEM alert fatigue through detection tuning, AI-driven investigations, and human security expertise. Rather than escalating every alert, Daylight investigates suspicious activity using security telemetry and business context to determine what requires action. This reduces unnecessary escalations and helps security teams focus on genuine threats instead of repetitive triage.
